
The Industrial Security Stack: Deconstructing the OT Security Market Platform
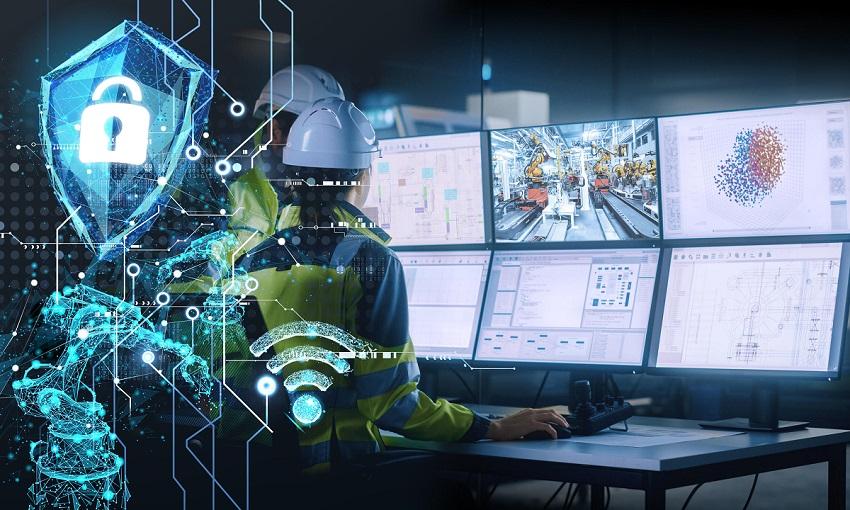
Protecting the complex and sensitive environments of factories and critical infrastructure requires a specialized and carefully designed technology stack. The modern Operational Technology Security Market Platform is an integrated system of hardware and software designed to provide visibility, threat detection, and risk management specifically for industrial control systems (ICS). This platform is fundamentally different from a traditional IT security platform. Its core design principle is to be completely passive and non-intrusive, ensuring that the security monitoring process can never interfere with or disrupt the critical physical operations being controlled. The architecture of this platform is focused on deep understanding of the unique protocols and behaviors of the OT world, allowing it to distinguish normal industrial processes from malicious cyber activity. Understanding the key layers of this platform—the passive visibility engine, the threat detection and analytics core, and the risk management and response layer—is essential to appreciating how industrial cyber defense is engineered.
The Foundational Platform: Passive Visibility and Asset Inventory
The bedrock of any OT security platform is its ability to provide deep and accurate visibility into the industrial network without actively scanning or "touching" the sensitive devices. This is achieved through passive network monitoring. The platform uses a network sensor (a physical or virtual appliance) connected to a SPAN or mirror port on a network switch to listen to all the OT network traffic. The platform's core engine then analyzes this traffic using a technique called Deep Packet Inspection (DPI). This DPI engine has a deep understanding of hundreds of proprietary industrial protocols (like Modbus, DNP3, S7, etc.). By analyzing this traffic, the platform can automatically create a detailed and accurate asset inventory, identifying every PLC, HMI, and engineering workstation on the network. It can also map out the entire network, showing which devices are communicating with each other and what protocols they are using. This foundational visibility is the essential first step; you cannot protect what you cannot see.
The Threat Detection and Analytics Core
Once visibility is established, the next critical layer of the platform is the threat detection and analytics engine. This is where the platform moves from simply identifying assets to detecting potential threats. This engine uses multiple techniques. Firstly, it uses signature-based detection to identify known malware and attack patterns specific to OT environments. Secondly, and more importantly, it uses behavioral and anomaly detection. The platform builds a baseline model of normal operational communication patterns on the network. It can then alert on any deviation from this baseline—for example, a controller receiving a command it has never received before, a device communicating at an unusual time of day, or an unauthorized laptop connecting to the engineering network. This allows the platform to detect novel or "zero-day" threats. Many platforms also integrate vulnerability management, correlating the discovered asset inventory with a database of known vulnerabilities in industrial equipment to identify and prioritize risks.
The Risk Management and Response Integration Layer
The final layer of the OT security platform is focused on managing risk and enabling a coordinated response. This layer provides a centralized dashboard where security analysts and plant operators can view alerts, investigate incidents, and understand the potential operational impact of a threat. The platform prioritizes alerts based on their severity and the criticality of the affected asset. A key part of this layer is its ability to integrate with the broader security and operational ecosystem. This means forwarding alerts and asset information to the organization's central IT SIEM platform, allowing the IT SOC to have visibility into OT events. It also involves integrating with IT firewalls and network access control (NAC) systems to enable response actions, such as quarantining a compromised device. In a more advanced use case, it might integrate with the plant's operational workflow systems, creating a work order for an engineer to physically inspect a device that is behaving anomalously. This integration layer is what bridges the gap between OT detection and enterprise-wide incident response.
➤ In-Depth Market Studies by Market Research Future:

 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek